


Cybersecurity moves fast. Either you uncover vulnerabilities before attackers do, or you’re left scrambling to contain the breach. Cybersecurity vulnerability assessment demands a proactive mindset, forcing you to think like an attacker, anticipate threats, and methodically reduce risk. Periodic cybersecurity vulnerability assessments allow you to identify, analyze, and prioritize security gaps across your infrastructure before attackers can exploit them.
White Paper
Why visibility is your first — and most critical — line of defense.
A cybersecurity vulnerability assessment is a systematic security evaluation that identifies, analyzes, and prioritizes potential security weaknesses across your IT infrastructure. Unlike penetration testing, which actively exploits vulnerabilities, vulnerability assessments focus on discovery and risk mitigation without attempting to breach systems.
Key components of a vulnerability assessment include:
This proactive security process helps organizations identify security gaps before attackers discover them, prioritize remediation efforts based on risk levels, maintain compliance with cybersecurity frameworks like NIST and ISO 27001, and reduce the overall attack surface of their systems.
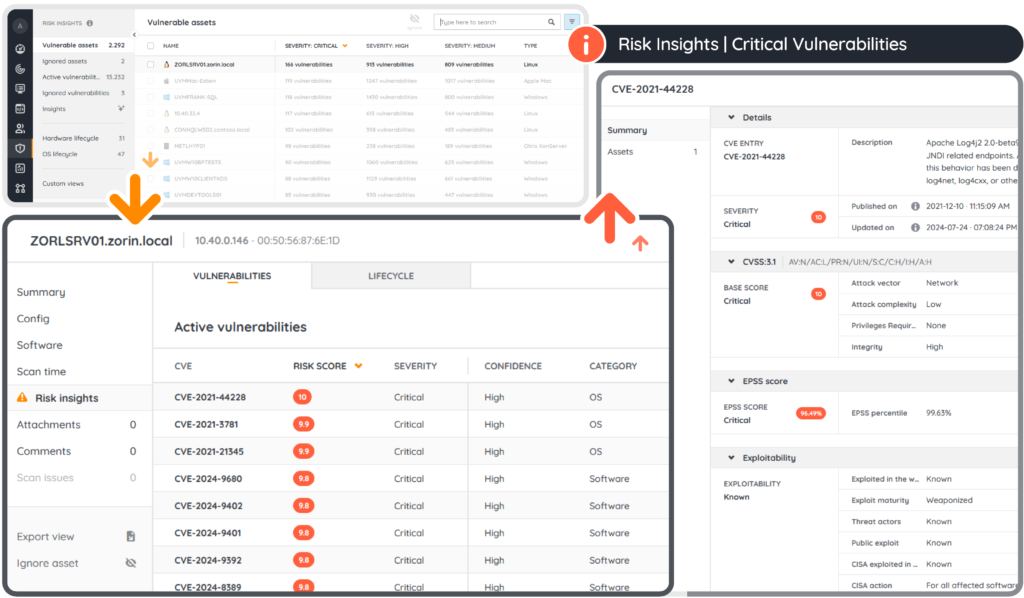
Vulnerability assessments are critical because cyber attackers automate their reconnaissance efforts. If your organization isn’t proactively scanning for vulnerabilities, you’re already at a disadvantage. Here’s why they matter:
Every system presents unique attack vectors, from misconfigured cloud instances to unpatched software and unmanaged devices. Different types of assessments target specific infrastructure components:
Network vulnerability assessments examine your network perimeter, including firewalls, routers, and switches for misconfigurations and security weaknesses. Automated scanning tools can detect common vulnerabilities, but manual validation remains essential for contextual analysis and accurate risk assessment. Blindly trusting scanner results is a dangerous security misstep.
Regular network assessments help maintain secure and resilient IT infrastructure while ensuring compliance with security standards.
Web applications often expose sensitive data through poorly secured APIs, authentication flaws, and misconfigured cloud storage. These assessments test for common vulnerabilities including:
Web application security testing tools like OWASP ZAP, Burp Suite, and manual code reviews should be integrated into your vulnerability analysis process.
Mobile applications face unique security challenges due to inconsistent patching and diverse operating environments. Common mobile vulnerabilities include:
Mobile security testing frameworks like MobSF and Drozer help uncover these threats before attackers exploit them.
Effective vulnerability assessment follows a strategic, two-step process that goes beyond simply running automated scans:
Start with comprehensive asset discovery. You cannot protect assets you don’t know exist. This process includes:
Not all vulnerabilities require immediate action. Effective prioritization considers:
For example, a missing patch on a public-facing web server requires immediate attention, while a vulnerability in an internal system with no known exploit may have lower priority.
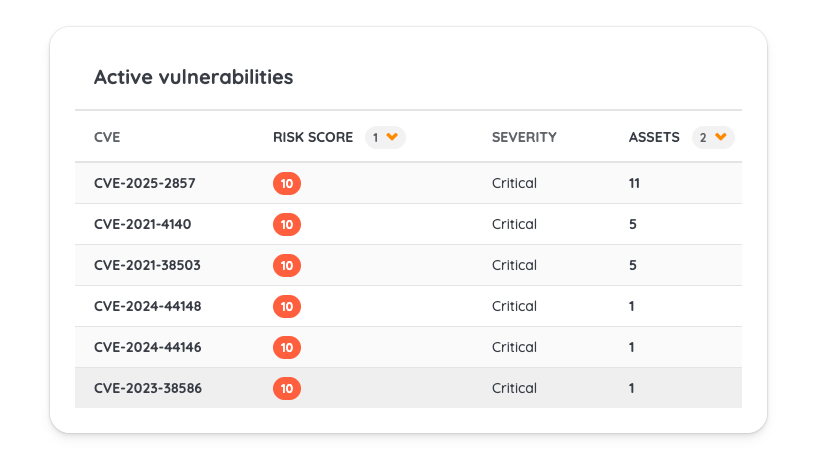
AI-driven solutions enhance traditional vulnerability assessment with:
Tools like Darktrace and Microsoft Defender leverage AI to help security teams identify risks faster. However, human expertise remains essential for interpreting findings, filtering false positives, and developing effective response strategies.
Effective vulnerability assessment goes beyond detection. It minimizes exploitability through strategic implementation:
1. Establish a Vulnerability Management Program
Create a structured program that ensures assessment results feed directly into patching workflows. This approach reduces exposure time and prevents critical fixes from being overlooked.
2. Maintain Regular Patching Schedules
Delayed patching remains one of the biggest security gaps. Critical vulnerabilities should be patched within 24-48 hours, as attackers often analyze security updates to craft exploits targeting unpatched systems.
3. Implement Secure Coding Practices
Security should begin at the development stage. Integrate static and dynamic application security testing (SAST/DAST) into CI/CD pipelines to identify vulnerabilities before deployment.
Vulnerability assessments should integrate seamlessly with broader cybersecurity initiatives:
Threat intelligence enriches vulnerability data by providing context about active threats. When threat intelligence identifies exploits targeting specific software versions in your environment, vulnerability assessments should reflect elevated risk levels.
Vulnerability assessments should inform incident response playbooks. Post-breach forensic analysis should validate whether vulnerability assessment processes effectively identified exploited weaknesses or require improvement.
Implement continuous scanning and monitoring rather than quarterly assessments. Attackers don’t wait for scheduled scans. Tools like CrowdStrike Falcon Spotlight and Tenable.io offer continuous assessment capabilities for real-time threat detection and remediation.
Without a complete inventory of your IT environment, vulnerabilities slip through the cracks. Lansweeper’s asset discovery and Risk Insights map every device, every piece of software, and every hidden risk, giving you the data you need to act fast. Stop chasing threats in the dark. Get a free demo today and take control of your security strategy.
Lansweeper Demo
Sit back and dive into the Lansweeper interface & core capabilities to learn how Lansweeper can help your team thrive.
OT vulnerability assessments should be conducted continuously through automated monitoring, with comprehensive manual assessments performed at least quarterly or whenever significant system changes occur. The frequency may increase based on regulatory requirements and threat landscape changes.
Vulnerability assessments identify and catalog security weaknesses without exploiting them, while penetration testing actively attempts to exploit vulnerabilities to demonstrate their impact. Vulnerability assessments are broader in scope and performed more frequently, while penetration testing provides deeper analysis of specific vulnerabilities.
Vulnerability assessment costs vary widely based on scope, methodology, and organizational size. Automated scanning tools range from free (OpenVAS) to thousands of dollars annually for enterprise solutions. Professional assessment services typically cost $5,000-$50,000 depending on infrastructure complexity and assessment depth.
Yes, small businesses can perform basic vulnerability assessments using automated tools like OpenVAS, Nessus Essentials, or cloud-based solutions. However, expert validation and manual testing often require cybersecurity expertise that may necessitate external consultation for comprehensive assessments.
Major compliance frameworks requiring regular vulnerability assessments include:
Prioritize vulnerabilities using the Common Vulnerability Scoring System (CVSS) combined with business context. Consider exploitability, asset criticality, and potential business impact. Address critical vulnerabilities on public-facing systems first, followed by high-risk internal systems based on data sensitivity and operational importance.
Blog

Explore Lansweeper for free.
No credit card required.