When companies are unsure how to demonstrate their cybersecurity efforts, many turn to ISO27001 and ISO27002. While these frameworks are great for showing compliance, they aren’t as effective for prioritizing, measuring, and implementing practical IT security initiatives. For this, a consensus-based framework like the CIS 18 Critical Security Controls® is ideal.
The CIS Controls® provide detailed, practical, and prioritized advice on implementing cybersecurity measures. They offer clear instructions on what actions to take, how to measure progress, prioritize efforts, and audit your cybersecurity posture.
In this article, we’ll explore the advantages of using CIS Controls, the common hurdles organizations might face, and best practices for successful implementation. Additionally, we’ll discuss how Lansweeper can aid in this process by providing essential tools for asset management and vulnerability assessment.
Center for Internet Security (CIS) Controls are a set of recommended actions and best practices designed to boost your organization’s cybersecurity. These controls are part of a framework created to protect systems and data from cyber threats.
Developed by a global community of cybersecurity experts, CIS Controls are regularly updated to tackle the latest threats and tech advancements.
CIS Controls are split into three categories:
CIS Controls v8, developed by the Center for Internet Security, is the latest version of prioritized cybersecurity best practices aimed at improving organizational security. This streamlined version consolidates 20 controls into 18, making them easier to implement and more relevant to current technology environments, including cloud and mobile. Designed to integrate with other cybersecurity frameworks like NIST, CIS Controls v8 provides actionable guidelines to manage and reduce cybersecurity risks effectively.
The main purpose of the Center for Internet Security (CIS) is to make the online world safer for everyone. CIS does this by developing best practices, guidelines, and tools to help organizations improve their cybersecurity. They create frameworks like the CIS Controls, which are step-by-step recommendations for securing IT systems and data.
By following these guidelines, organizations can better protect themselves against cyber threats and reduce their overall risk.
Adhering to CIS Controls comes with a bunch of benefits that can really boost your organization’s cybersecurity. Here are some key perks:
CIS Controls focus on three key aspects of cybersecurity to protect IT environments effectively:
By focusing on these key components, you can build a strong foundation for your cybersecurity efforts.
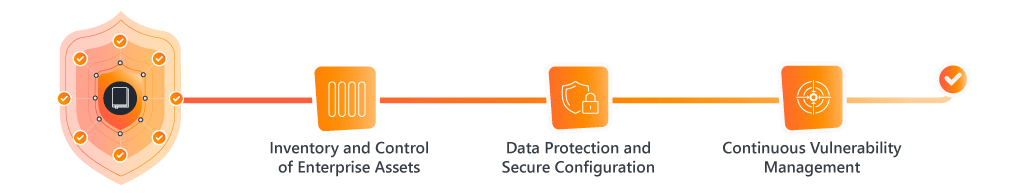
Implementing CIS Controls can significantly boost your organization’s cybersecurity, but it’s not without its challenges.
One of the biggest challenges is having enough resources—whether it’s time, money, or personnel. Smaller organizations, in particular, might struggle to allocate the necessary resources to fully implement and maintain all the controls. Prioritizing the most critical controls and gradually expanding your efforts can help manage this issue. Maintaining accurate and up-to-date data about your IT assets is crucial but can be tricky, especially in dynamic environments where assets are constantly changing. Regular audits and automated tools can help, but they require ongoing effort and attention.
Integration with existing IT systems and tools can be complex and time-consuming, often requiring custom integrations or middleware solutions, which can be costly and require specialized knowledge. Ensuring smooth integration without disrupting current workflows is a delicate balancing act. For CIS Controls to be effective, they need buy-in from all stakeholders, not just the IT department. This involves clear communication, adequate training, and demonstrating the value of the controls. Additionally, staying current with evolving cyber threats requires continuous monitoring, regular updates, and staying informed about the latest security trends. By being aware of these challenges, you can better prepare and strategize for successful CIS Controls implementation.
Here are some best practices to ensure a smooth and successful implementation:
When choosing a cybersecurity framework, organizations often weigh the CIS Controls list against frameworks like the NIST Cybersecurity Framework. CIS Controls offer a set of specific, actionable best practices that provide detailed guidance on improving security, while the NIST framework offers a broader, more flexible approach with its five core functions: Identify, Protect, Detect, Respond, and Recover, designed to be adaptable across various industries.
CIS standards can complement other standards such as NIST or ISO/IEC 27001, integrating with them to form a comprehensive security strategy. This integration allows organizations to address both strategic and operational aspects of cybersecurity, creating a robust and resilient security posture that caters to immediate and long-term risk management needs.
The Center for Internet Security (CIS) website offers a comprehensive range of resources to enhance cybersecurity, including detailed CIS Controls and Benchmarks, the CIS-CAT Pro assessment tool, free implementation guides, CIS Hardened Images for secure cloud deployments, and automated tools for continuous monitoring. It also features the CIS WorkBench for community collaboration, self-assessment tools like CSAT, and an Ambassadors Program for expert guidance.
These resources collectively help organizations improve their cybersecurity posture and comply with CIS standards.
Lansweeper supports CIS implementation and compliance with automatic discovery and inventory of all hardware and software assets in your network.
Lansweeper’s discovery and inventory capabilities align with CIS Control 1 (Inventory and Control of Hardware Assets) and CIS Control 2 (Inventory and Control of Software Assets), ensuring you have an accurate and up-to-date picture of your IT environment.
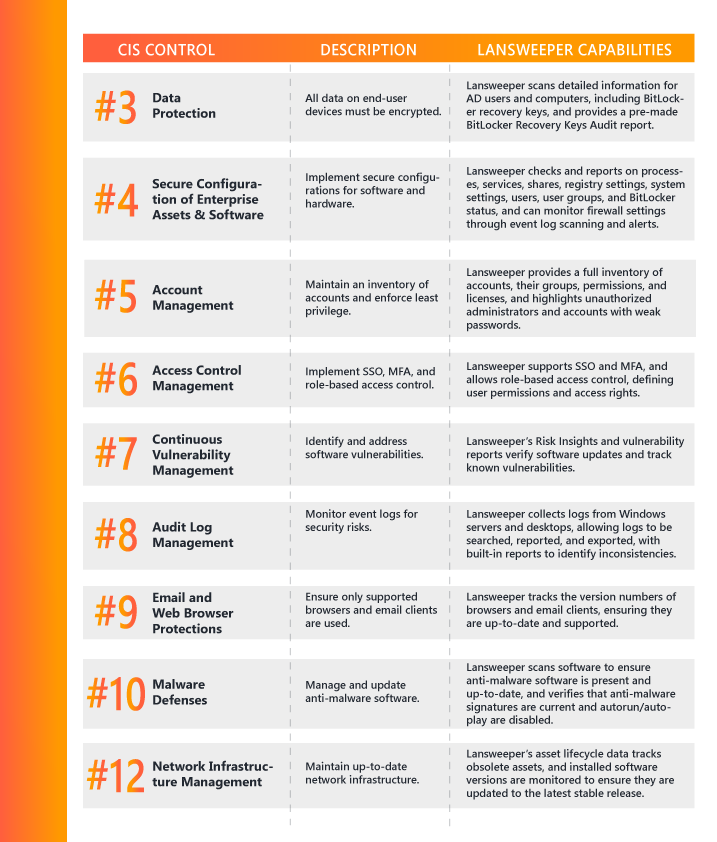
See the table below for more information about how Lansweeper aligns with other CIS Controls:
Implementing CIS Controls is essential for bolstering your organization’s cybersecurity. While it comes with both benefits and challenges, following best practices can ensure a successful implementation. With Lansweeper, you can effectively implement and manage CIS Controls, boosting your cybersecurity posture and minimizing the risk of cyber threats.
To see how Lansweeper can enhance your cybersecurity efforts and ensure your compliance with CIS Controls, book a demo today and start identifying vulnerabilities in your IT environment.
Blog
Explore Lansweeper for free.
No credit card required.