Integrations

ThreatQ Asset & Vulnerabilities Integration

The Lansweeper CDF integration ingests Lansweeper asset and vulnerability data into ThreatQ to support asset-centric analysis and risk visibility.

The Lansweeper CDF integration ingests Lansweeper asset and vulnerability data into ThreatQ to support asset-centric analysis and risk visibility. Assets are mapped to asset objects with related network identifiers as attributes, while vulnerabilities are ingested as vulnerability objects and linked back to their associated assets. This seamlessly correlates asset and vulnerability data with sightings and external intelligence.

The integration provides the following feeds:

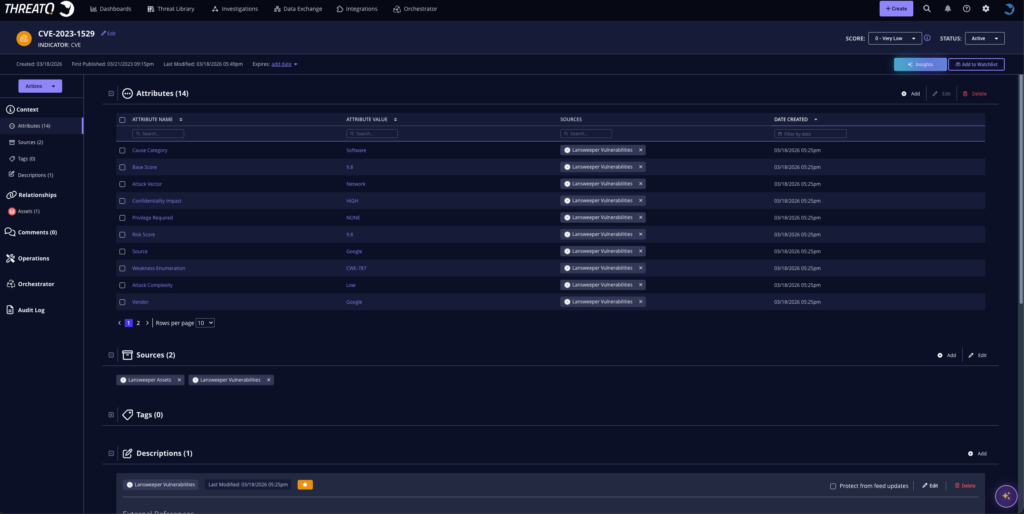
  • Lansweeper Assets – ingests asset data and related indicators.
  • Lansweeper Vulnerabilities – ingests vulnerability data and links it to assets.

The integration ingests the following object types:
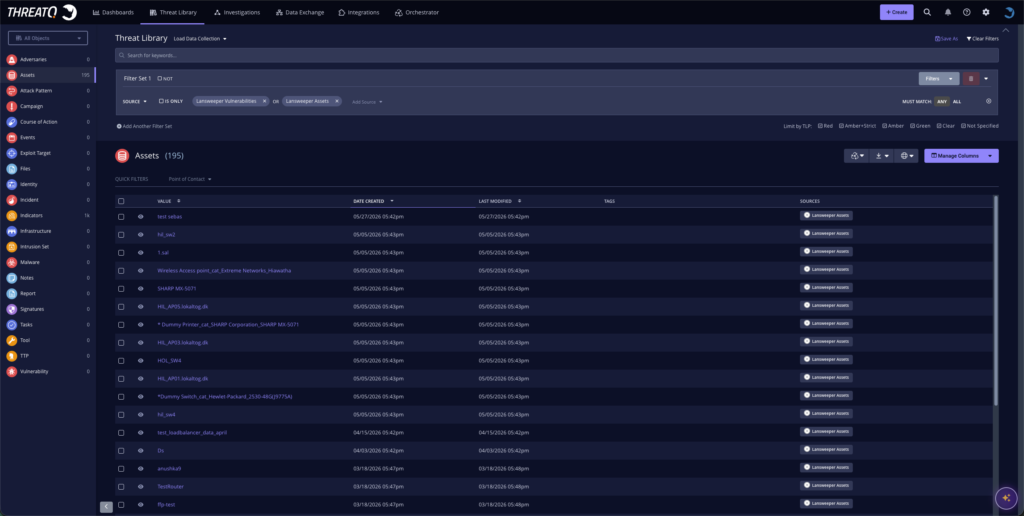
  • Assets
  • Asset Attributes
  • Indicators
  • Vulnerabilities
  • Vulnerability Attributes
Screenshot 2026 06 05 at 11.45.02 AM
Screenshot 2026 06 05 at 11.43.56 AM

Key Integration Features

  • Ingestion of asset information, including context.
  • Ingestion of vulnerability information, either as vulnerabilities or indicators.
  • User-selected controls over exactly which fields are ingested into your Threat Library.

Requirements

  • Lansweeper Pro or Enterprise License
  • ThreatQ versions >= 5.12.0

Documentation

Support

Ready to get started?

Explore Lansweeper for free.
No credit card required.

Need help evaluating?
Get guidance on pricing at scale and enterprise requirements.
Talk to sales
Clear pricing as you grow
Transparent plans that scale with your environment.
View plans & pricing